Atlassian Flaw Exploited, Ransomware Firm Fraud, DarkSword Steals Crypto
Quick Answer
Cybersecurity news from October 6–12, 2026, highlights exploited software vulnerabilities, ransomware fraud, crypto theft, malware campaigns, and AI security risks. Organizations should patch critical flaws, strengthen email security with DMARC, SPF, and DKIM, and improve threat detection.
This week was dominated by zero-day exploitation, arrests tied to the ShinyHunters group, and a record quarter for ransomware. Several attacks targeted widely used enterprise tools, including Atlassian, Fortinet and Zammad, while Google, OpenAI and Cisco Talos flagged new abuse of AI and certificate infrastructure.
Atlassian Data Center flaw exploited within hours of disclosure!
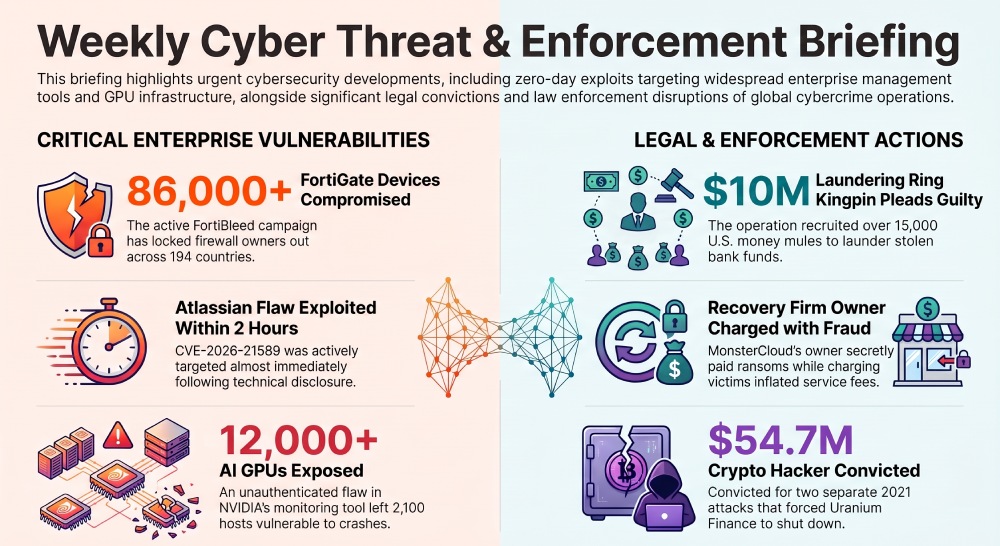
A critical arbitrary file access flaw, CVE-2026-21589 (CVSS 9.3), affects several Atlassian Data Center products, including Confluence, Jira and Bitbucket. Attackers began exploiting it about two hours after watchTowr published technical details. Source: The Hacker News
Ransomware recovery firm owner charged with fraud!
Zohar Pinhasi, owner of Florida-based MonsterCloud, was charged with wire fraud. Prosecutors allege he claimed he could restore victims’ data without paying ransoms, but instead paid the ransoms and charged fees well above the original demands. Source: The Hacker News
New DarkSword iOS exploit kit variant steals crypto wallet data!
A new variant called P7 DarkSword can extract Keychain data directly on the iPhone and supports two-way command and control. It is also better at hiding itself, which makes older indicators of compromise less useful. Source: The Hacker News
Russia-aligned group keeps refining its MATCHBOIL malware!
The threat actor UAC-0099 is updating MATCHBOIL, a downloader that now runs every two minutes instead of once. That lets it keep pulling new payloads from its control server, and the group is targeting the Ukrainian government. Source: The Hacker News
FBI disrupts China-linked Flax Typhoon infrastructure!
The FBI and Department of Justice disrupted tools and domains used by Flax Typhoon, a China-linked group. The tools included Microscan for reconnaissance and FishHub for spear-phishing and follow-on payloads. CISA warned the group is positioned in critical infrastructure, including operational technology systems. Source: The Hacker News
Third ShinyHunters arrest announced!
The FBI said it arrested another suspected co-conspirator of ShinyHunters, the group linked to the FBIjobs.gov incident on a third-party vendor’s platform. Court documents and journalist Brian Krebs reported the person is Edward Dubrovsky, a Toronto-based executive, though the FBI has not named him. Source: The Hacker News
Attackers obtained Google certificates by hijacking country-code domains!
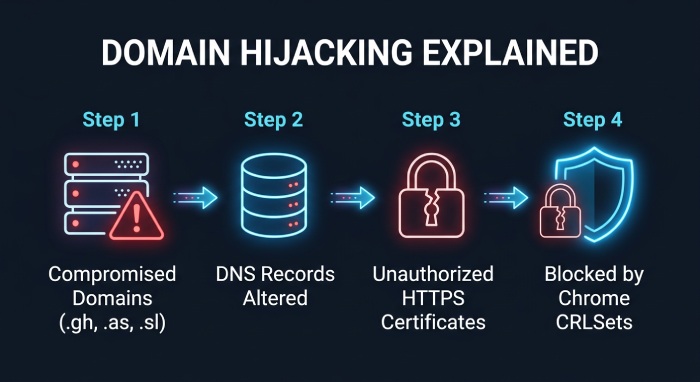 Attackers compromised third-party operators of the .gh (Ghana), .as (American Samoa) and .sl (Sierra Leone) domains, changed DNS records, and obtained unauthorized HTTPS certificates for several Google domains and other organizations. Chrome blocked the certificates through CRLSets. Source: The Hacker News
As cyber threats continue to evolve, implementing DMARC, SPF, and DKIM is essential for strengthening email security, preventing domain spoofing, and reducing the risk of phishing attacks.
Flaw in GoBalance load balancer let attackers take over Tor sites!
A vulnerability in GoBalance, software used by many darknet sites, allowed attackers to recover a site’s master signing key from public data. Between 5 and 7 October, both onion addresses of the Dread darknet forum were taken over and redirected to a rival platform. Source: The Hacker News
Let’s Encrypt shortens default certificate lifetimes!
Let’s Encrypt announced that default TLS certificate lifetimes will drop from 90 to 64 days starting February 2027, ahead of planned 45-day lifetimes in 2028. Site owners should plan their renewal automation now. Source: Let’s Encrypt
Microsoft CEO calls for emergency brakes on advanced AI models!
In a lengthy post on X, Satya Nadella argued that AI can no longer be treated as a set of black boxes. He said organizations must assume a model could be compromised and be able to pause or shut it down mid-task. Source: Satya Nadella on X
Money laundering kingpin pleads guilty!
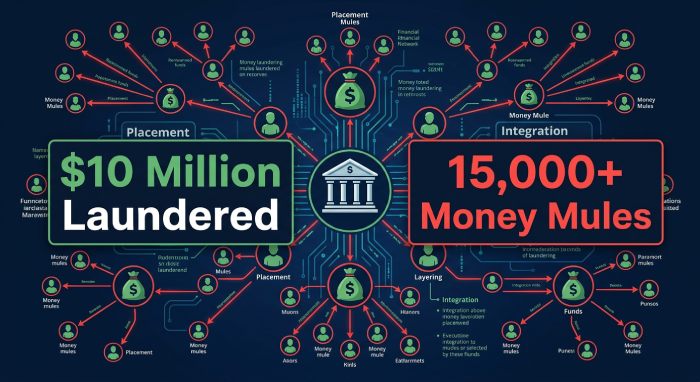
Ukrainian-Russian dual citizen Oleg Korniev pleaded guilty to running an international money laundering organization. It recruited more than 15,000 US money mules and laundered at least $10 million stolen from over 750 US bank accounts. Source: US Department of Justice
Crypto exchange hacker convicted!
A US jury convicted Jonathan Spalletta of computer fraud and money laundering for two 2021 attacks on Uranium Finance. Prosecutors say he took about $1.4 million in the first hack and about $53.3 million in the second, which caused the exchange to shut down. Source: US Department of Justice
OpenAI disrupts Russian and Iranian influence campaigns!
OpenAI said it disrupted two operations, one from Russia (Dark Clark) and one from Iran (Bogus Bylines), that used ChatGPT to create fake journalist personas and covert think tanks. Some of their articles appeared in outlets with large audiences. Source: OpenAI
Malware now tries to trick AI analysis tools!
Cisco Talos found malware families, including FRUITSHELL, PLOTSAFE, HOLLOWCLAD and MANTLEMAZE, that embed natural-language instructions aimed at automated AI analysis. Some code comments even claim the sample is a monitored honeypot, so AI-assisted analysis needs safeguards. Source: Cisco Talos
Critical NVIDIA GPU monitoring flaw exposes AI infrastructure!
CVE-2026-47483 (CVSS 8.2) in NVIDIA’s DCGM Exporter lets unauthenticated attackers crash the service by flooding it with requests. Lava Security found about 2,100 hosts exposing the tool without authentication, leaking telemetry from more than 12,000 GPUs. Version 4.8.2 fixes it. Source: Lava Security
Three new malware loaders spotted in the wild!
Researchers reported 2CLoader, which delivers Vidar, Remus Stealer and XWorm; AvisLoader, which arrives via ClickFix lures and uses an encrypted peer-to-peer network to fetch commands; and Sauron Loader, sold to Russian-speaking cybercriminals. Source: Zscaler
Akira ransomware attack traced step by step!
Huntress investigated a September 2026 Akira attack. The attacker got in over Remote Desktop Protocol, disabled antivirus, used Rclone to steal data, and then deployed ransomware, while a GOST tunneling tool helped maintain persistence. Source: Huntress
FortiBleed campaign locks owners out of Fortinet firewalls!
The FBI and Secret Service warned on October 6 that the FortiBleed campaign remains active. SOCRadar counts more than 86,000 compromised FortiGate devices in 194 countries, and attackers sometimes change or delete original admin accounts to lock owners out. Source: DIESEC
General Manager
General Manager of DuoCircle. Product strategy and commercial lead for AutoSPF's 2,000+ customer base.
LinkedIn Profile →